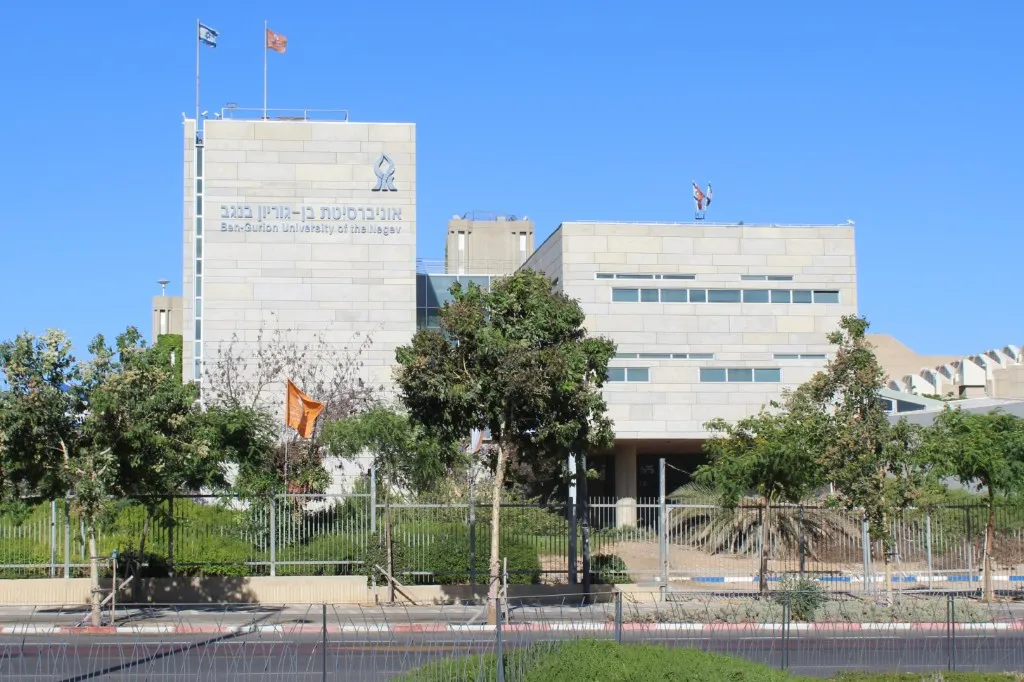
Jerusalem, 16 November, 2026 (TPS-IL) — A new study led by Ben-Gurion University of the Negev has exposed vulnerabilities in the digital screening systems used by synthetic DNA manufacturers, warning that potentially dangerous genetic sequences can be disguised and ordered online by splitting them into smaller, seemingly harmless fragments.
The researchers also developed a new algorithm designed to identify such concealed threats, offering a potential upgrade to biosecurity measures as genetic engineering becomes increasingly accessible.
Custom-made DNA is widely used by universities, pharmaceutical companies and biotechnology firms to develop medicines, study diseases, engineer microorganisms and produce proteins. However, the technology also creates a biosecurity challenge: the same ordering systems can potentially be exploited to obtain genetic material that could be used to produce dangerous biological substances.
The findings, published in the peer-reviewed journal Nature Communications, highlight the challenges facing an industry in which customers can order custom-made DNA sequences online and have them delivered directly to their laboratories.
Synthetic DNA companies routinely screen customer orders for sequences associated with dangerous biological agents, including toxins. However, existing screening standards generally require suspicious sequences to exceed a minimum length, typically 50 consecutive genetic building blocks, known as nucleotides.
Researchers led by Prof. Rami Pozis and Prof. Isana Wexler-Lublinsky found that this requirement creates a potential loophole. By dividing a dangerous sequence into shorter fragments, an attacker could evade detection because no individual fragment exceeds the screening threshold. Once delivered, the fragments could potentially be reassembled using standard laboratory techniques to recreate the original toxin-producing sequence.
‘Attackers are Becoming More Sophisticated’
The research team developed an algorithm called Gene Edit Distance (GED) to address the vulnerability. Rather than examining each DNA fragment independently, the algorithm evaluates whether multiple fragments within an order could be combined or modified to produce a known toxic sequence.
“Attackers are becoming more sophisticated, so defense systems must also advance accordingly,” said Shaked Tiuri-Atia, the master’s student who led the study.
“Instead of just looking at each segment individually and asking ‘Is it toxic?’, the GED algorithm estimates the ‘effort’ that would be required of a biologist to reassemble the toxin in the laboratory. It is this broad perspective that allows us to block disguised threats,” she explained.
To test existing screening capabilities, the researchers created a database of toxin sequences and applied three concealment strategies: inserting harmless DNA between fragments, rearranging or reversing fragments, and distributing fragments among several genetic structures within a single order.
They then evaluated two commercial screening tools, the open-source SeqScreen system, the widely used BLAST sequence-alignment tool, and their GED algorithm against concealed and unaltered toxin sequences, as well as harmless genetic sequences.
The commercial systems and SeqScreen generally detected threats when at least one fragment exceeded 50 nucleotides, consistent with current regulatory guidelines. However, three sequences containing fragments longer than that threshold were missed. The companies responsible for the screening tools are investigating the discrepancies.
BLAST struggled to distinguish between harmless sequences and concealed toxin sequences. GED, by contrast, achieved 100 percent accuracy in separating the two groups, without generating false positives, according to the study.
The researchers said the algorithm also addresses a major challenge in screening short DNA fragments: many short sequences occur naturally and are not dangerous. By combining multiple fragments into longer queries, GED can identify potential threats while reducing false alarms.
“This study is an example of a proactive penetration test, which aims to examine security vulnerabilities and allow biotech companies to fix them before hostile actors begin to exploit them,” Prof. Pozis said.
The researchers have shared their database of concealed sequences with international organizations, including the International Gene Synthesis Consortium (IGSC) and the Synthetic Biology Research Consortium (SBRC), to help improve industry screening standards.
“The message is clear: the more accessible biology is to the public, the tighter its digital protective envelope must be,” Pozis said.
The GED algorithm’s source code has been made publicly available.